Who can change what
Each user can only update data they have permission to modify.
The Designer role sets up Excel documents and controls which tables, columns, and rows users can update. Users with the Data Editor role can only update the data made available by the Designer. Data Editors cannot change the document's configuration or permissions.
SQL Spreads connects to the database using the user's Windows or Microsoft Entra ID account, or their SQL Server login. Alternatively, each Excel document can be configured to use a shared SQL Server login.
Change tracking can record who changed each row and when. SQL Server temporal tables can also be used to maintain a full history of data changes.
Data Storage
SQL Spreads is downloadable software installed on your users’ desktop machines. SQL Spreads works directly with data stored either on your on-premises servers or in your organization’s cloud databases, such as Azure SQL.
SQL Spreads does not store customer data outside of your infrastructure.
All data is stored and processed on your own machines, cloud accounts, and databases. The company behind SQL Spreads does not access, process, or store your business data.
Authentication
SQL Spreads relies on industry-standard Windows, SQL Server, and Microsoft Entra ID security. SQL Spreads does not implement its own user management or authentication layer for database access.
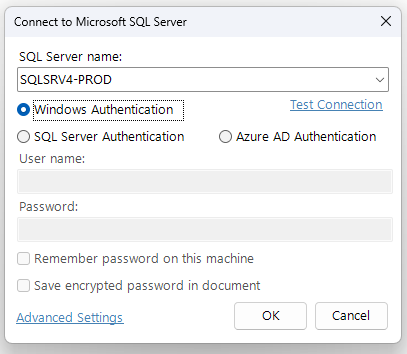
The SQL Spreads Excel Add-In supports the following authentication methods for SQL Server:
- Windows Authentication
- SQL Server Authentication
- Microsoft Entra ID Authentication (including MFA support)
We recommend following Microsoft’s best practices by using Windows Authentication or Microsoft Entra ID Authentication whenever possible.
Independent Penetration Testing
SQL Spreads has undergone independent penetration testing performed by an external security firm.
The assessment covered:
- SQL Spreads Excel Add-In
- SQL Spreads License Manager
The penetration test was conducted using recognized industry methodologies and best practices, including:
- OWASP
- MITRE
- NIST
- CREST
- NIS
All findings identified during the assessment were remediated, and the remediation work was verified during a retesting phase.